A hacking demo published on 16 November shows a WordPress server falling to one crafted request through the PHP flaw known as PHP2Shell. The demo makes its point, but its frame was already out of date: three days after it went up, PHP shipped 7 more critical fixes, two of them finishing October’s repair and one slipping past it.
Table of Contents
Any PHP server that was updated once in October and then left alone is behind again. On 19 November 2026 the PHP project released versions 8.5.13, 8.4.28, 8.3.37 and 8.2.36, fixing 17 vulnerabilities, 7 of them rated critical. Two of those critical fixes complete the repair of CVE-2026-109619, one of the two PHP2Shell flaws patched in an emergency on 21 October. A third, named phpAfterShell by the firm that found it, gets around the October fix through the same session upload feature attackers used the first time. For a language that still runs 68.1% of the websites whose server-side code W3Techs can identify, the lesson is blunt: one patch did not close PHP2Shell.
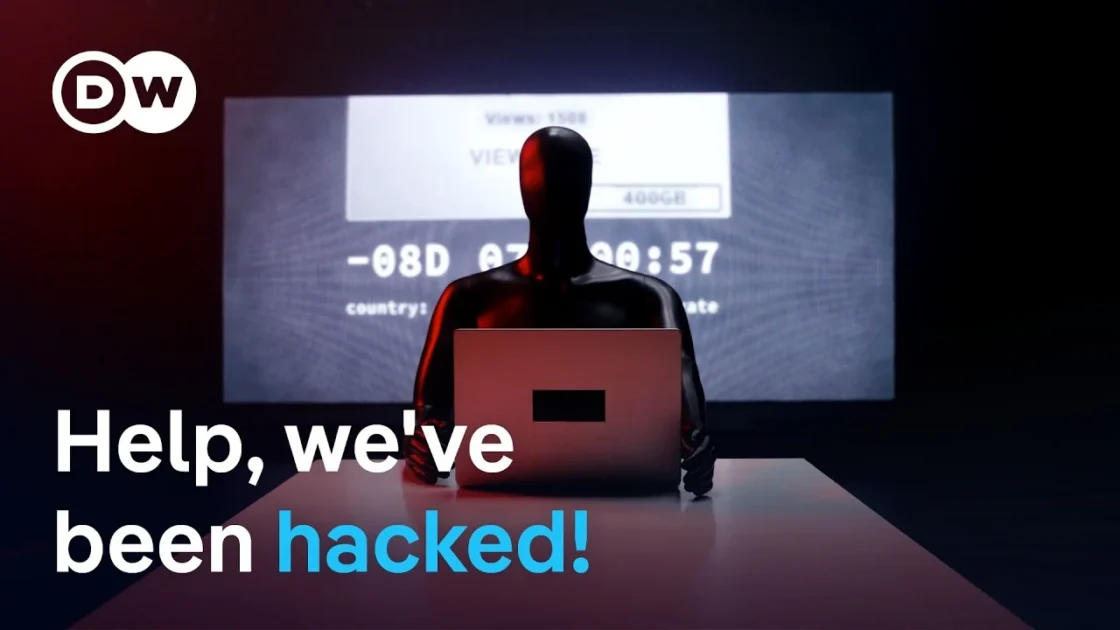
The best-known recent example of how the bug is being shown to the public is a video of about 15 minutes from the Neurix channel, published on 16 November, which walks through scanning, exploiting and taking over a WordPress test server. It is an educational demonstration by an independent channel, not material from the PHP project or from the researchers who found the flaws, and its description carries the usual warning to test only systems you own. Its core message holds. Several facts around it do not, and a viewer who patched to the newest version on the day it appeared was missing fixes three days later.
A WordPress takeover built on one crafted request
The video’s description lays out the attack in chapters, from finding the target to total control. The listed tools are Kali Linux as the attacking machine, WordPress on PHP 8.3.12 as the victim, a public PHP2Shell scanner, a proof-of-concept exploit labelled Chain A, and session.upload_progress named as the vulnerable feature. The promise is that one specially crafted request is enough to take the server, dump the database and leave with every customer record, without a password.
The central claim is consistent with the official record. PHP’s advisory, as reported by LWN, said every installation serving web requests was at risk, highest on Apache with mod_php, where an unauthenticated request can trigger the attack before any application code runs. The PHP Foundation adds that full remote code execution was demonstrated on mod_php with default settings and confirmed on PHP-FPM through application code paths.
The victim version matters more than the video lets on. The October fix for that branch was 8.3.36 and the November one is 8.3.37, so the demo server sits 24 point releases behind the first repair.
Three details in the description that need correcting
The description says PHP powers nearly 78% of the web. That figure is old. W3Techs measured 77.7% on 1 January 2023 and 68.1% on 20 November 2026, and its figure only covers sites whose server-side language it can detect. The share is still huge, and falling every year.
The description also says the flaw sat in PHP for fourteen years and was finally found in October 2026. The first half fits: Wikipedia’s account dates the affected versions back to PHP 5.4, released in 2012. The second half does not. According to the PHP Foundation, a core developer found the first signs of the out-of-memory problem in 2024 while fixing an issue from an external audit funded by Germany’s Sovereign Tech Agency. Calif reported an unconditional remote code execution with the same root cause on 11 August 2026, Wiz followed on 24 August and OpenAI on 18 September. October is when the flaw became public, after the CVE numbers leaked on 20 October and the release was pulled forward to 21 October.
Finally, the claim that attackers struck within hours of discovery understates the timeline. Amazon Threat Intelligence logged an exploitation attempt on 17 October, four days before public disclosure, from a commercial anonymization network, and says it remains unclear how that actor got the details.
Upload progress was the doorway and memory handling the flaw
Calling session upload progress “the vulnerable feature” mixes up the door with the lock. The two October bugs sit deeper. CVE-2026-109618 is triggered when a request hits PHP’s memory limit at exactly the wrong moment, leaving half-built internal data that request cleanup later treats as valid. CVE-2026-109619 leaves internal state pointing at memory that belonged to an earlier request, so the next request on the same worker can use memory that was already freed. The PHP Foundation says both live in memory management and error handling, code nearly every request touches, which made a safe fix hard to agree on.
Upload progress mattered because it let an unauthenticated multipart request reach those paths before the site’s own code ran, which is why the official stopgaps begin with switching it off.
The delay has a paper trail. The Foundation writes that its security team could not choose between competing fixes and that work stalled for months, adding that “the delay was a structural failure”. A second thread runs further back. In October 2020 a user filed PHP bug #80291, warning that the default session handler writes session files non-atomically and can leave them corrupted if a write is interrupted. Commenters dismissed it, and the ticket still reads Open. Researchers at depthfirst built phpAfterShell on that kind of interrupted write, according to Precursor Security’s account of their report. Linking the two is this article’s interpretation, but the pattern is hard to miss: a known weakness waited until someone weaponised it.
The October patch left work for November
The 19 November release turns the PHP2Shell story from a single emergency into a sequence. Precursor Security’s tracking of the PHP advisories lists 17 CVEs with advisories, seven rated critical at a CVSS 4.0 score of 9.2. Two of them are explicit follow-ups: CVE-2026-129481, which the PHP team describes as an incomplete fix for CVE-2026-109619 and which affects PHP 8.3 and later, and CVE-2026-129182, a further use-after-free in the same fatal-error backtrace on PHP 8.5.
The third is phpAfterShell, CVE-2026-126714. Depthfirst says it started as a review of the October patch, which stopped objects being created while PHP handled upload progress but did not make the session file write itself safe. With file-based sessions and upload progress, both PHP defaults until this release, an interrupted write can splice old and new session data so that the next ordinary page load reads attacker-chosen objects. The fix empties the file before writing, and the new releases switch upload progress off by default unless a php.ini, FPM pool or hosting panel turns it back on.
No exploitation of the November flaws had been reported on release day, and none had entered CISA’s catalogue of exploited vulnerabilities. One practical trap remains. Linux distributions often backport fixes without changing the version number, so php -v proves little on its own.
Real attacks hit gateways harder than ordinary websites
The video’s picture of one request emptying a customer database fits a lab better than the evidence so far. Kaspersky, citing Censys data on 3 November, counted 29 million of 46 million scannable servers still running a vulnerable PHP build almost two weeks after the patches, yet found no wave of mass breaches. Its explanation: working exploits must match the exact PHP build, memory settings and request handling. In the Palo Alto Networks case first reported by Dream, Kaspersky notes, the attackers chose about 240 of roughly 19,000 exposed devices, the ones running versions their exploit could handle.
Where attackers did succeed, the targets were uniform appliances. Check Point Research reported that from 30 October, about a week after the fix, an attacker used PHP2Shell against unpatched Mobile Access portals on Check Point Security Gateways, escalated to root through a separate flaw, CVE-2026-123039, planted web shells and in some Israeli organisations moved to VMware ESXi hosts and ran a wiper. A wider second wave followed on 2 November. Check Point says the evidence does not allow a confident attribution.
That is the exposure a WordPress demo does not show. The Dutch NCSC tracks PHP inside 972 vendor products, and on 12 November listed 212 as vulnerable and 213 as fixed, warning that administrators often cannot update the PHP inside an appliance themselves.
Checks for site owners and their agencies this week
Visitors cannot fix any of this, as TechRadar notes. For a business on shared hosting or a managed WordPress plan, the first question goes to the host: which PHP build serves the site, and does the vendor advisory name the November CVEs. The target is 8.2.36, 8.3.37, 8.4.28 or 8.5.13, or a distribution package that lists those fixes.
Old branches are the hard case. W3Techs puts 24.6% of PHP sites on version 7 and 7.3% on version 5, nearly a third between them. PHP published source backports for 7.4, 8.0 and 8.1 in October, but versions 8.1 and older get no November fixes, so the realistic options are an upgrade to a supported branch or a vendor that maintains backports.
Three cheap steps help while upgrades wait. Set session.upload_progress.enabled = 0 unless the site needs it, and search every php.ini, FPM pool and virtual host for an explicit setting that turns it back on. Review logs for multipart POST requests carrying PHP_SESSION_UPLOAD_PROGRESS and for HTTP 500 errors with out-of-memory messages, and, following Amazon’s advice, start any investigation from 17 October, not from the disclosure date. Then list every appliance, NAS and control panel that bundles PHP, because those patches arrive on the vendor’s schedule. Amazon’s broader warning applies to all of it: “A 7-day or 30-day SLA assumes a delay that no longer exists.”
PHP security still rests on a small team
The PHP Foundation’s own account is the strongest corrective to the idea of a sudden discovery. It says security work on a language behind government services, shops and banks still depends on a small group of funded developers and volunteers. Since 1 July the security team has published 15 CVEs and worked through more than 100 invalid or duplicate reports, a load the Foundation links to AI-assisted research. Commentary in The Guardian, cited by Wikipedia, put the Foundation at 13 full- and part-time staff.
The disclosure showed how thin the margins are. The CVE numbers leaked on 20 October with a wrong severity score of 10.0, and on 21 October Chainguard shipped patched images more than six hours before the coordinated release, letting anyone study the fix.
The video is right that PHP2Shell is serious and that unpatched servers can be taken over. It is out of date on the scale, the history and the fix. Two developments would change the picture from here: phpAfterShell appearing in CISA’s exploited list, which would mean the November release becomes as urgent as October’s, and the major Linux distributions shipping their November packages, which decides how fast most servers can actually catch up.
Author:
Jan Bielik
CEO & Founder of Webiano Digital & Marketing Agency
This article is an original analysis supported by the sources cited below
How Hackers Exploit the New PHP Bug (PHP2Shell)
The Neurix video of 16 November 2026 whose description lists the WordPress on PHP 8.3.12 target, the tools used and the claims tested here.
Today’s PHP Security Release, and How We’re Strengthening PHP Security
The PHP Foundation’s account of both October flaws, the 2024 discovery, the stalled fix, the August reports, the leak and its staffing limits.
PHP patches released for two critical RCEs
Relays the official PHP advisory on who was at risk, the highest risk on mod_php and the fixed October versions.
PHP Bug #80291: Data corruption and data loss in default session handler
The 2020 report that PHP’s default session handler writes files non-atomically, dismissed in comments and still listed as open.
Historical yearly trends in the usage statistics of server-side programming languages
Shows PHP falling from 77.7% of detectable websites in January 2023 to 68.1% on 20 November 2026.
Usage statistics of PHP for websites
Breaks down PHP sites by major version, with 24.6% on version 7 and 7.3% on version 5 in November 2026.
Amazon Threat Intelligence identifies PHP2Shell exploitation prior to public disclosure in MadPot
Documents the 17 October exploitation attempt before disclosure, the detection markers and the advice to measure patch timelines in hours.
PHP2Shell Exploitation on Check Point Gateway
Check Point Research on attacks from 30 October against unpatched gateways, the root escalation, web shells, ESXi wiper and uncertain attribution.
php2shell vulnerabilities (CVE-2026-109618, CVE-2026-109619)
The Dutch NCSC inventory of 972 products that embed PHP, with vulnerable and fixed counts as of 12 November 2026.
PHP2Shell
Summarises affected versions back to PHP 5.4 from 2012, the leaked CVSS score and commentary on the Foundation’s 13 staff.
PHP2Shell: what we know about the threat two weeks later
Gives the Censys count of 29 million unpatched servers, the lack of mass breaches and why exploits must match each build.
No, the internet isn’t dying due to one of the most significant vulnerabilities of 2026
Explains that patching falls to site owners and hosts rather than visitors, and flags the risk on unsupported PHP branches.
phpAfterShell and the November PHP Security Release (7 Critical CVEs)
Tracks the 19 November release, the incomplete October fix, depthfirst’s phpAfterShell bypass and the new upload progress default.
| Citing this article? Brief excerpts are welcome. Please credit Webiano.digital, name the author where stated, and include a link to https://webiano.digital and to this original article. Full or substantial republication requires prior written permission. Read our Copyright and Content Use Policy. |
This article was prepared with the assistance of artificial intelligence tools. The content underwent expert human review, and Webiano Digital & Marketing Agency assumes editorial responsibility for its final version and publication.